Social Media Hacking Isn’t Random, It’s Data-Driven
You don't have to click a malicious link to become a target. Sometimes, all it takes is posting online. Most people think of hacking as a technical crime, like someone breaking through firewalls, deploying malware, or cracking passwords. But a growing number of cyberattacks begin long before any of that, with a criminal quietly studying your public social media activity.
Your posts, check-ins, job history, connections, and even the quizzes you take are raw material for a highly personalized attack.
This is data-driven social engineering, and it's one of the most effective forms of cybercrime operating today. This article takes you behind the scenes to show exactly how cybercriminals analyze your social media data and what you can do to make yourself a much harder target.
What Are Social Media Analytics and How Do Hackers Use Them?
Step 1: How Hackers Collect Public Social Media Data (OSINT)
Step 2: Mapping Your Relationships and Professional Network
Step 3: Analyzing Your Behavior, Habits, and Posting Patterns
Step 4: Identifying Weak Points and Security Vulnerabilities
Step 5: Putting It All Together: From OSINT to Exploit
How AI and Automation Make Social Media Targeting Easier Than Ever
Why Data-Driven Social Engineering Works So Well
How to Reduce Your Risk of Social Media Profiling
Conclusion: Hacking Through Social Media Isn’t Going Anywhere
What Are Social Media Analytics and How Do Hackers Use Them?
Social media analytics is the process of gathering and analyzing data from social media platforms such as Facebook, Instagram, and LinkedIn to extract insights about behavior, trends, interactions, and sentiment. The data you collect is generally publicly available: posts, comments, shares, connections, geolocation, timestamps, etc.
Although social media analytics is widely used in marketing, customer support, and reputation monitoring, it’s also a useful tool for hackers.
Cybercriminals don’t need to access your social media accounts to attack you anymore. Now, they can use machine learning combined with public social media data to tailor highly effective, individualized attacks. Here’s a quick rundown of how they do it:
- Reconnaissance and target profiling
- Crafting personalized social engineering attacks with the data they’ve gathered
- Building trust by mapping a target’s social media network
- Automating and scaling data extraction
This is known as data-driven social engineering. Unlike brute force hacking or malware exploits, this tactic targets human behavior and exploits trust to get victims to divulge sensitive information willingly. Social media analytics was originally developed for marketing and research, but it’s become a valuable tool in the hands of threat actors.
Let’s take a look at the step-by-step process cybercriminals use to leverage social media analytics for their scams and illegal activities.
Step 1: How Hackers Collect Public Social Media Data (OSINT)
The first phase of a modern social media-based attack is open-source intelligence (OSINT) gathering. This process involves collecting and analyzing data from publicly accessible sources to build actionable intelligence. Law enforcement, security, and threat analysts use OSINT extensively.
Cybercriminals use it for:
- Web scraping and automated tools to gather posts and profile data
- Searching multiple platforms (LinkedIn, Facebook, Instagram) for information about life events, employment, contacts, and interests
- Collecting metadata like geotags and timestamps that reveal routines and locations
This raw data then becomes their foundation for profiling and eventually attacking you.
Step 2: Mapping Your Relationships and Professional Network
Once the hackers have your data, they start mapping your network and relationships. If you’re their target, they’ll try to figure out who your connections are, such as:
- Colleagues and reporting relationships
- Friends, family members, or close contacts
- External partners who work with your organization
Hackers create this social graph of you so they can define the power structures, points of influence, and communication channels you use with the people in your life.
Why are they doing this? They impersonate the people you trust, reaching out to you and pretending to be a colleague, a teammate from your slowpitch softball league, or an old friend.
Step 3: Analyzing Your Behavior, Habits, and Posting Patterns
Now that hackers have the raw data and network maps, they can apply social media analytics and behavioral analysis to see:
- When you’re most active online
- Which topics you post about or engage with
- Your emotional cues, language patterns, and interests
This step involves looking for patterns, so that they can craft messaging that feels personal or legitimate. Marketers use the same process to build ideal customer profiles, or the type of person most likely to buy their products. Threat actors use it to send messages that sound specific, so they seem less suspicious.
Step 4: Identifying Weak Points and Security Vulnerabilities
At this stage in the process, the cyber attacker’s analysis is almost complete. They use the profile of you that they’ve aggregated to identify weak points, such as:
- Answers to common security questions embedded in posts (e.g., pet names, hometowns)
- Patterns of oversharing that reveal sensitive dates or habits
- Cross-referenced data from breach lists and public records
They look for this information so they can use it to guess or reset your passwords, bypass secondary authentication challenges, or tailor their social engineering attempts to exploit specific psychological triggers.
Step 5: Putting It All Together: From OSINT to Exploit
Turning OSINT into meaningful vulnerabilities is what elevates a random scam into a highly targeted exploit. Once they complete all the steps in this process, attacks typically proceed with one of several strategies:
- Personalized lures that reference real content (spear phishing)
- Posing as a trusted contact based on network maps
- Fabricating believable scenarios using real personal details
- Using social clues to steal credentials or take over accounts
So why is it helpful for you to understand this process?
Because it proves that simply hiding some information isn’t enough. Hackers aren’t just collecting the data; they’re aggregating, analyzing, and exploiting it. This is a major shift for modern cybercrime and social engineering scams.
How AI and Automation Make Social Media Targeting Easier Than Ever
OSINT and social media profiling by hackers aren’t new. But this information gathering was extremely time-consuming, requiring cybercriminals to manually scroll through profiles and piece together information. The scale of these types of attacks was naturally limited.
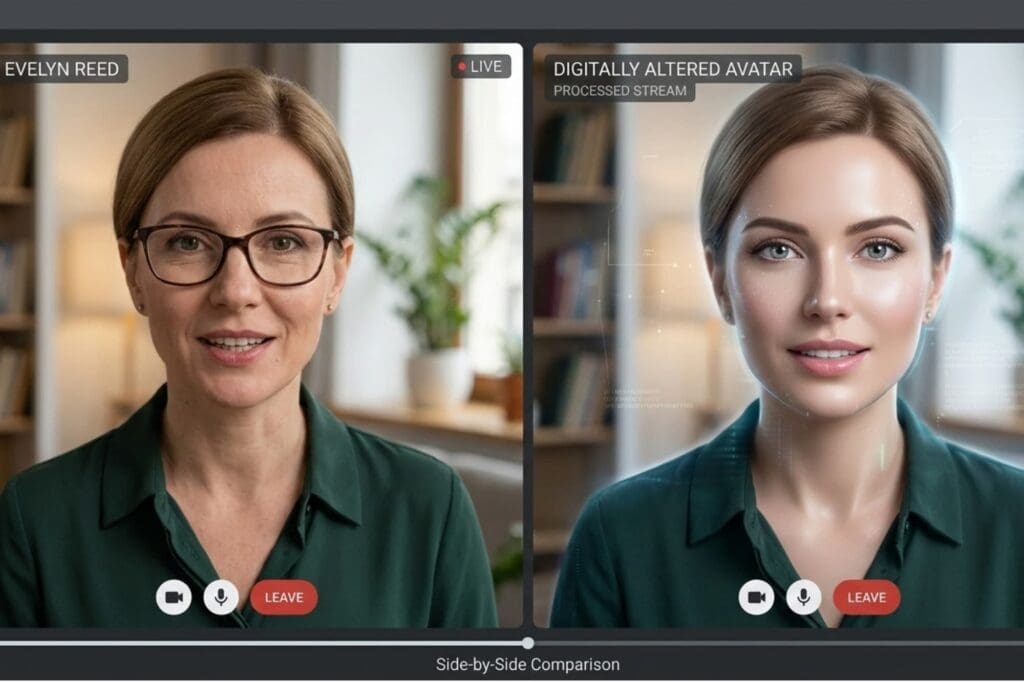
AI and automation have essentially removed this constraint, however. Now, cybercriminals can automate the information gathering and analysis to scale their attacks. AI bots can crawl public data, digital footprints, leaked credentials, and social media. Meanwhile, generative models can craft personalized spear-phishing text or deepfake voices for high-value targets.
Hackers most often use social media analytics to launch phishing attacks and AI now plays a big role. When you consider that 82.6% of phishing emails use AI, or that 78% of people opened phishing emails written by AI (and 21% of those clicked on the email’s malicious link), you can see how much AI truly boosts hackers’ efforts to scam and attack individuals.
Deepfakes: When Your Own Voice and Face Become Weapons
AI doesn't just improve text-based attacks. It has created an entirely new category of threat that wouldn't exist without social media: deepfakes built from your publicly posted photos, videos, and audio. In the first quarter of 2025 alone, penetration testing firm DeepStrike recorded 179 deepfake incidents, surpassing the total for all of 2024 by 19%.
The financial consequences are severe. A finance employee at global engineering firm Arup was invited to a video conference to discuss a confidential and urgent transaction. Their initial suspicion was overcome when they joined the call…but every participant was a deepfake. The company lost $25 million.
Lowering the Barrier to Entry
AI hasn't just made existing criminals more effective; it has made cybercrime accessible to people who previously lacked the technical skills to attempt it. Agentic security operations platform BlinkOps has reported that new sections dedicated to AI have appeared on hacking forums and networks that are pushing cybercriminals to discover how it can empower different attack vectors.
Sophisticated, personalized social media-based attacks are no longer the exclusive domain of well-resourced criminal organizations. They're available to anyone willing to pay for a tool. Social media analytics gave attackers the blueprint, and AI gave them the factory to act on it at scale.
Why Data-Driven Social Engineering Works So Well
When social engineering tactics are backed by data, they’re more effective. They exploit human psychology rather than tech flaws, because humans tend to respond emotionally and instinctively.
All of that data also allows cybercriminals to personalize their messages to a much greater extent. As a result, their outreach feels familiar and credible, and builds trust. They also rely on social cues and authority signals in their messages because familiar names and roles enhance believability.
Thanks to AI, these messages are precise and expertly constructed, which makes them more realistic and hard to spot as fake.
Ultimately, although we’d like to believe that we’re logical and rational beings, humans are the weak link in data-driven, social-media-analytics-powered cyberattacks. Our emotional and social behavior still outweighs rational defenses.
How to Reduce Your Risk of Social Media Profiling
If attackers are using publicly available data, then your best defense is to limit what you share publicly online. Let’s go through it in more detail.
Start by Understanding Your Own Exposure
Before you can reduce your risk, you need to know what’s already out there. Google your own name, including image search, to see what comes up and go from there. Treat yourself as a target and ask: what could someone build from what they find?
Lock Down Your Privacy Settings
The fix starts with your social media privacy settings, but it requires ongoing attention rather than a one-time adjustment. On Facebook, use the Privacy Checkup tool to review settings like audience control and profile visibility. On Instagram, switch to a private account, limit who can see your stories, and adjust device permissions to restrict access to your camera, microphone, and location.
Be Deliberate About What You Share
Privacy settings only control who sees your content. The other half of the equation is what you put out in the first place. Avoid posting your location in real time. For example, share vacation photos after you're home, not while you're away. Your location data may reveal information about your schedule and routine, people you regularly associate with, and areas you frequently visit, such as your workplace, home, or place of worship.
Those fun quizzes, games, and memes on social media might seem harmless, but they can be a way for companies or scammers to collect your personal data.
Be Strategic About What You Share Professionally
LinkedIn deserves particular attention because it's where professional exposure is greatest and where users tend to be least guarded. Threat actors scan employee social media profiles on platforms like Facebook, X, and Instagram to gather personal details, while job postings on vacancy websites can reveal network infrastructure, technology stacks, and organizational structure. Be thoughtful about the level of detail you share.
Manage Your Connections Carefully
Be selective about who you add to social networks. Only accept friend or connection requests from known and trusted individuals. Exercise caution when dealing with unknown or suspicious profiles, as these could be fronts for cybercriminals aiming to access your data or infiltrate your network.
Remove Old Accounts and Request Data Broker Opt-Outs
Though not in use, old shopping and social media accounts still contain your financial and personal information. Instead of risking a potential breach in one of those accounts, delete or deactivate them.
Go further by addressing data brokers, which aggregate and sell your personal information to virtually anyone. Data brokers hosting your information may be legally obligated to remove your data when requested. You can even use a tool like Incogni to request removal in bulk.
Turn on 2FA and Use Strong Passwords
Use strong, unique passwords for each account, enable two-factor authentication, and regularly review your account activity for unauthorized access. If an attacker has profiled you and attempts to access your accounts using information gathered from your social media, a strong unique password and 2FA can stop that attempt cold even when the underlying data has already been harvested.
Conclusion: Hacking Through Social Media Isn’t Going Anywhere
Social media profiling doesn't require a sophisticated breach or a stolen password. It requires nothing more than the information you've already made public. The good news is that unlike many cybersecurity threats, this is one where your own behavior is the most powerful defense.
You don't need to disappear from the internet. You need to be deliberate about what you share, who can see it, and how the pieces connect across platforms. Tighten your privacy settings, think before you post, and remember that hackers aren't reading your profiles, they're analyzing them. The less data they have to work with, the less effective their attacks will be.